IAS 2
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/67

There's no tags or description
Looks like no tags are added yet.
Name | Mastery | Learn | Test | Matching | Spaced | Call with Kai | Chat |
|---|
No analytics yet
Send a link to your students to track their progress
68 Terms
Phishing
Browser-based Attacks;
Redirect users to fake web pages that mimic trustworthy sites, asking them to submit their personal information.
Mobile users are more likely to be victims of phishing sites because the devices are small in size and they display only short URLs, limited warning messages, scaled-down lock icons, and so on.
Framing
Browser-based Attacks;
Involves a web page integrated into another web page using the iFrame elements of HTML.
An attacker exploits iFrame functionality used in the target website, embeds his/her malicious web page, and uses clickjacking to steal users’ sensitive information.
Clickjacking
Browser-based Attacks;
Also known as a user interface redress attack
Is a malicious technique used to trick web users into clicking something different from what they think they are clicking
Man-in-the-Mobile
Browser-based Attacks;
An attacker implants malicious code into the victim’s mobile device to bypass password verification systems that send one-time passwords(OTPs) via SMS or voice calls.
Thereafter, the malware relays the gathered information to the attacker.
Buffer Overflow
Browser-based Attacks;
An abnormality whereby a program, while writing data to a buffer, surfeits the intended limit and overwrites the adjacent memory. This results in erratic program behavior, including memory access errors, incorrect results, and mobile device crashes
Data Caching
Browser-based Attacks;
Data caches in mobile devices store information that is often required by these devices to interact with web applications, thereby preserving scarce resources and resulting in better response time for client applications. Attackers attempt to exploit these data caches to access the sensitive information stored in them.
Baseband Attacks
Phone/SMS-based Attacks;
Attackers exploit vulnerabilities in a phone’s GSM/3GPP baseband processor, which sends and receives radio signals to cell towers.
SMiShing
Phone/SMS-based Attacks;
A phishing fraud in which an attacker uses SMS to send text messages containing deceptive links to malicious websites or telephone numbers to a victim.
The attacker tricks the victim into clicking the link or calling the phone number and revealing his or her personal information.
Sensitive Data Storage
Application-based Attacks;
Some apps installed and used by mobile users employ weak security in their database architecture, which makes them targets for attackers who seek to hack and steal the sensitive user information stored in them.
No Encryption/Weak Encryption
Application-based Attacks;
Apps that transmit unencrypted or weakly encrypted data are susceptible to attacks such as session hijacking
Improper SSL Validation
Application-based Attacks;
Security loopholes in an application’s SSL validation process may allow attackers to circumvent the data security.
Configuration Manipulation
Application-based Attacks;
Apps may use external configuration files and libraries that can be exploited in attack. This includes gaining unauthorized access to administration interfaces and configuration stores, as well as the retrieval of clear-text configuration data.
Dynamic Runtime Injection
Application-based Attacks;
Attackers manipulate and abuse the run time of an application to circumvent security locks and logic checks, access privileged parts of an app, and even steal data stored in memory.
Unintended Permissions
Application-based Attacks;
Misconfigured apps can sometimes open doors to attackers by providing unintended permissions.
Escalated Privileges
Application-based Attacks;
Attackers engage in privilege escalation attacks, which take advantage of design flaws, programming errors, bugs, or configuration oversights to gain access to resources that are usually protected from an application or user.
No Passcode/Weak Passcode
The System;
Many users choose not to set a passcode or use a weak PIN, passcode, or pattern lock, which an attacker can easily guess or crack to compromise sensitive data stored in the mobile device.
iOS Jailbreaking
The System;
The process of removing the security mechanisms set by Apple to prevent malicious code from running on the device. It provides root access to the OS and removes sandbox restrictions. Thus, jailbreaking involves many security risks as well as other risks to iOS devices, including poor performance, malware infection, and so on.
Android Rooting
The System;
Allows Android users to attain privileged control (known as “root access”) within Android’s subsystem. Like jailbreaking, rooting can result in the exposure of sensitive data stored in the mobile device.
OS Data Caching
The System;
An OS cache stores used data/information in memory temporarily on the hard disk.
An attacker can dump this memory by rebooting the victim’s device with a malicious OS and extract sensitive data from the dumped memory.
Passwords and Data Accessible
The System;
iOS devices store encrypted passwords and data using cryptographic algorithms that have certain known vulnerabilities. Attackers exploit these vulnerabilities to decrypt the device’s Keychain, exposing user passwords, encryption keys, and other private data
Carrier-loaded Software
The System;
Pre-installed software or apps on devices may contain vulnerabilities that an attacker can exploit to perform malicious activities such as deleting, modifying, or stealing data on the device, eavesdropping on calls, and so on.
User-initiated Code
The System;
_______ is an activity that tricks the victim into installing malicious applications or clicking links that allow an attacker to install malicious code to exploit the user’s browser, cookies, and security permissions.
Wi-Fi (weak encryption/no encryption)
The Network;
Some applications fail to encrypt data or use weak algorithms to encrypt data for transmission across wireless networks. An attacker may intercept the data by eavesdropping on the wireless connection.
Although many applications use SSL/TLS, which offers protection for data in transit, attacks against these algorithms can expose users’ sensitive information
Rogue Access Points
The Network;
Attackers install an illicit wireless access point by physical means, which allows them to access a protected network by hijacking the connections of legitimate network users.
Packet Sniffing
The Network;
An attacker uses sniffing tools such as Wireshark and Caps a Network Analyzer to capture and analyze all the data packets in network traffic, which generally include sensitive data such as login credentials sent in clear text.
Man-in-the-Middle (MITM)
The Network;
Attackers eavesdrop on existing network connections between two systems, intrude into these connections, and then read or modify the data or insert fraudulent data into the intercepted communication
Session Hijacking
The Network;
Attackers steal valid session IDs and use them to gain unauthorized access to user and network information.
DNS Poisoning
The Network;
Attackers exploit network DNS servers, resulting in the substitution of false IP addresses at the DNS level. Thus, website users are directed to another website of the attacker’s choice.
SSLStrip
The Network;
A type of MITM attack in which attackers exploit vulnerabilities in the SSL/TLS implementation on websites. It relies on the user validating the presence of the HTTPS connection. The attack invisibly downgrades connections to HTTP without encryption, which is difficult for users to detect in mobile browsers.
Fake SSL Certificates
The Network;
________ represent another type of MITM attack in which an attacker issues a fake SSL certificate to intercept traffic on a supposedly secure HTTPS connection.
The Data Center / CLOUD
have two primary points of entry: a web server and a database.
Platform Vulnerabilities
Web-server-based Attacks;
Attackers exploit vulnerabilities in the OS, server software (e.g., IIS), or application modules running on the web server. They may monitor communication between a mobile device and the web server to expose protocol or access control flaws
Server Misconfiguration
Web-server-based Attacks;
A misconfigured server may allow attackers to gain unauthorized access to resources.
Cross-site Scripting (XSS)
Web-server-based Attacks;
Exploits vulnerabilities in dynamically generated web pages, allowing attackers to inject malicious client-side code (JavaScript, VBScript, ActiveX, HTML, or Flash) into legitimate websites.
Cross-Site Request Forgery (CSRF)
Web-server-based Attacks;
Tricks an authenticated user’s browser into sending unauthorized requests to a trusted site, compromising the session integrity
Weak Input Validation
Web-server-based Attacks;
Attackersforge communications or bypass application logic to exploit missing validation checks. This can lead to XSS, buffer overflow, injection attacks, and system malfunction
Brute-Force Attacks
Web-server-based Attacks;
Attackers use trial-and-error to guess valid input fields(e.g., passwords). Systems that allow unlimited attempts are highly vulnerable.
Other examples include cross-origin resource sharing exploits, side-channel attacks, hypervisor attacks, and VPN-targeted exploits.
SQL Injection
Database Attacks;
Attackers use non-validated input to inject SQL commands through a web application for execution by the backend database, granting unauthorized access or retrieving information directly.
Privilege Escalation
Database Attacks;
Exploits to gain high-level database access, allowing attackers to steal sensitive data.
Data Dumping
Database Attacks;
Forces the database to dump data, revealing sensitive records
OS Command Execution
Database Attacks;
Attackers inject OS-level commands into database queries, potentially gaining root-level access to the host system.
Mobile Attack Vectors
vectors make mobile phone platforms susceptible to malicious attacks both from the network and upon physical compromise.
Given below are some ofthe attack vectorsthat allow an attacker to exploit vulnerabilitiesin mobile OS, device firmware, or mobile apps:
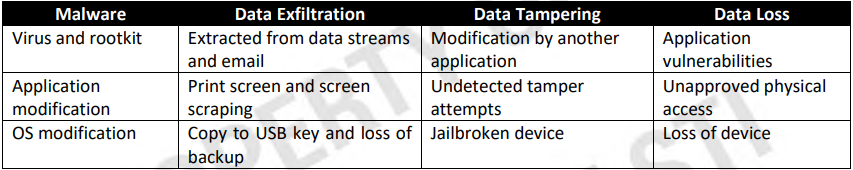
Mobile Platform Vulnerabilities and Risks
Malicious Apps in Stores
Mobile Malware
App Sandboxing Vulnerabilities
Weak Device and App Encryption
OS and App Update Issues
Jailbreaking and Rooting
Mobile Application Vulnerabilities
Privacy Issues (Geolocation)
Weak Data Security
Excessive Permissions
Weak Communication Security
Physical Attacks
OWASP
Open Worldwide Application Security Project
M1 — Improper Platform Usage
OWASP Top 10 Mobile Risks;
This category covers the misuse of a platform feature or the failure to use platform security controls
It includes Android intents, platform permissions, and the misuse of Touch ID, Keychain, orsome other security control that is part of the mobile device’s OS.
M2 — Insecure Data Storage
OWASP Top 10 Mobile Risks;
Arises when development teams assume that users and malware will not have access to a mobile device’s file system and subsequently to sensitive information in the device’s data stores.
“Jailbreaking” or rooting a mobile device bypasses encryption protection mechanisms. OWASP recommends analyzing platforms’ data security application programming interfaces (APIs) and calling them appropriately.
Unintended data leakage occurs when a developer unintentionally places sensitive data in a location on the mobile device that is easily accessible by other apps on the device. Such leakage is normally caused by vulnerabilities in the OS, frameworks, compiler environment, new hardware, and so on, without a developer’s knowledge. It is a significant threat to the OS, platforms, and frameworks; thus, it is important to understand how they handle features such as URL caching, browser cookie objects, and HTML5 data storage.
M3 — Insecure Communication
OWASP Top 10 Mobile Risks;
This category covers poor handshaking, incorrect SSL versions, weak negotiation, cleartext communication of sensitive assets, and so on. Such flaws expose an individual user’s data and can lead to account theft. If the adversary intercepts an admin account, the entire site could be exposed.
A poor Secure Socket Layer (SSL) setup can also facilitate phishing and man-in-the-middle (MITM) attacks.
M4 — Insecure Authentication
OWASP Top 10 Mobile Risks;
This category captures notions of authenticating the end user or bad session management, such as:
Failing to identify the user when it is required
Failure to maintain the user’s identity when it is required
Weaknesses in session management
M5 — Insufficient Cryptography
OWASP Top 10 Mobile Risks;
The code applies cryptography to a sensitive information asset. However, cryptography is insufficient in some ways.
This category covers issues in which cryptography is attempted but not performed correctly. This vulnerability will result in the unauthorized retrieval of sensitive information from the mobile device. To exploit this weakness, an adversary must successfully convert encrypted code or sensitive data into its original unencrypted form due to weak encryption algorithms or flaws in the process of encryption.
M6 — Insecure Authorization
OWASP Top 10 Mobile Risks;
This category captures failures in authorization (e.g., authorization decisions on the client side and forced browsing). It is distinct from authentication issues (e.g., device enrolment and user identification)
When an app does not authenticate users at all in a situation where it should (e.g., granting anonymous access to some resource or service when authenticated and authorized access is required), then it is an authentication failure and not an authorization failure.
M7 — Client Code Quality
OWASP Top 10 Mobile Risks;
This category covers “Security Decisions via Untrusted Inputs” and is one of the less frequently used categories. It is the catch-all for code-level implementation problems in the mobile client, which are distinct from server-side coding mistakes.
It captures buffer overflows, format string vulnerabilities, and various other code-level mistakes where the solution is to rewrite some code that is running on the mobile device.
Most exploitations that fall into this category result in foreign code execution or DoS on remote server endpoints (and not the mobile device itself).
M8 — Code Tampering
OWASP Top 10 Mobile Risks;
This category covers binary patching, local resource modification, method hooking, method swizzling, and dynamic memory modification.
Once an application is delivered to a mobile device, its code and data resources are resident on the device. An attacker can directly modify the code, change the memory contents dynamically, change or replace the system APIs that the application uses, or modify the application’s data and resources. Thus, the attacker can directly subvert the intended use of the software for personal or monetary gain.
M9 — Reverse Engineering
OWASP Top 10 Mobile Risks;
This category includes the analysis of the final core binary to determine its source code, libraries, algorithms, and other assets.
Software such as IDA Pro, Hopper, otool, and other binary inspection tools give the attacker insights into the inner workings of the application. Thus, he/she may exploit other nascent vulnerabilities in the application and uncover information about backend servers, cryptographic constants and ciphers, and intellectual property.
M10 — Extraneous Functionality
OWASP Top 10 Mobile Risks;
Often, developers include hidden backdoor functionality or other internal development security controlsthat are not intended to be released into a production environment. For example, a developer may accidentally include a password as a comment in a hybrid app. Another example involves the disabling of two-factor authentication during testing.
Typically, an attacker seeks to understand extraneous functionality within a mobile app to discover hidden functionality in the backend systems. Attackers will typically exploit such extraneous functionality directly from their own systems without any involvement by the end users.
General Guidelines for Mobile Platform Security
Do not load too many applications, and avoid auto-upload of photos to social networks
Perform a security assessment of the application architecture
Maintain configuration control and management
Install applications from trusted application stores
Securely wipe or delete the data when disposing of the device
Do not share the information within GPS-enabled apps unless it is necessary
Never connect two separate networks, such as Wi-Fi and Bluetooth, simultaneously
Disable wireless access, such as Wi-Fi and Bluetooth, if not in use
Ensure that your Bluetooth is “off” by default. Turn it on whenever it is necessary
Disable wireless access, such as Wi-Fi and Bluetooth, if not in use, to avoid illegal wireless access to the device
Disable sharing/tethering Internet connections over Wi-Fi and Bluetooth when not in use
Use Passcode
General Guidelines for Mobile Platform Security;
Configure a strong passcode with the maximum possible length to gain access to your mobile devices
Set an idle timeout to automatically lock the phone when not in use
Enable the lockout/wipe feature after a certain number of attempts
Consider an eight-character complex passcode
Thwart passcode guessing: set erase data to ON
Update OS and Apps
General Guidelines for Mobile Platform Security;
Update OS and apps to keep them secure
Apply software updates when new releases are available
Perform regular software maintenance
Enable Remote Management
General Guidelines for Mobile Platform Security;
In an enterprise environment, use MDM software to secure, monitor, manage, and support mobile devices deployed across the organization
Do not allow Rooting or Jailbreaking
General Guidelines for Mobile Platform Security;
Ensure that your MDM solutions prevent or detect rooting/jailbreaking
Include this clause in your mobile security policy
Use Remote Wipe Services
General Guidelines for Mobile Platform Security;
Use remote wipe services such as Find My Device (Android) and Find My iPhone or FindMyPhone (Apple iOS) to locate your device should it be lost or stolen
Report a lost or stolen device to IT so that they can disable certificates and other access methods associated with the device
Encrypt Storage
General Guidelines for Mobile Platform Security;
If supported, configure your mobile device to encrypt its storage with hardware encryption
Use device encryption and patch applications
Encrypt the device and backups
Perform periodic backup and synchronization
General Guidelines for Mobile Platform Security;
Use a secure, over-the-air backup-and-restore tool that performs periodic background synchronization
(Android) Back up to your Google account so that sensitive enterprise data is not backed up to the cloud
Control the location of backups o Encrypt backups
Keep sensitive data off shared mobile devices. If enterprise information is locally stored on a device, then it is recommended that this device not be openly shared
Limit logging data stored on the device
Use a secure data-transfer utility or encrypt data in transit to or from the device, to ensure confidentiality and data integrity
Malwarebytes Security
Mobile Security Tools;
An antimalware mobile tool that provides protection against malware, ransomware, and other growing threats to Android devices.
It blocks, detects, and removes adware and malware; conducts privacy audits for all apps; and ensures safer browsing.
Lookout Personal
Mobile Security Tools;
A mobile security app that offers protection against malware, phishing, and device theft, along with backup and system monitoring features.
Zimperium’s zIPS
Mobile Security Tools;
An enterprise-grade mobile threat defense solution that detects and prevents advanced mobile attacks in real time.
BullGuard Mobile Security
Mobile Security Tools;
A mobile protection tool providing antivirus, antitheft, and backup features for Android devices.
Norton Security for iOS
Mobile Security Tools;
A mobile security app that safeguards iOS devices from phishing, unsafe WiFi networks, and online threats.
Comodo Mobile Security
Mobile Security Tools;
A comprehensive mobile security solution offering antivirus protection, privacy protection, and real-time threat detection.