Database Security
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/26

There's no tags or description
Looks like no tags are added yet.
27 Terms
What is database security?
subset of cubersecurity thatdeals specifically with databases
protects DBMS & DB against intentional/accidental threats
What does database security concern?
protection from theft, mishandling. damage to hardware/software/data
maintenance of service to avoid disruptions & misdirection
What is Anderson’s Rule summarised?
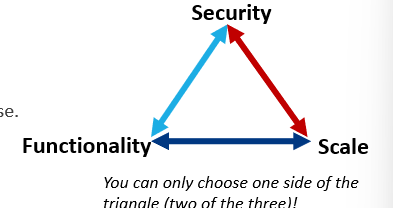
systems that handle sensitive personal ingo involve trilemma of security, functionality and scale - which you can only choose two
trilemma is getting the balance right
more accessible + usable DB = more vulnerable to security threats
more secure + protected DB from threats = more difficult to access & use
How can we reduce the risk to the security of database systems?
by applying sensible security policies & protocols
conduct security audit
What do we identify with a security audit?
security vulnerabilities + threats
measures to protect the systems & data against thos vulnerabilities
What are the core objects of the security of data?
CIA Triad
Confidentiality
ensure info is only accesible to authorised persons
Integrity
consistency, trustworthiness & accuracy of data
Availability
reilable access to info by authorised users when needed
Database security requires strategies & measures to ensure what 4 things?
USERS identifiable,authorised + monitored
DATA protected, tamperproof,auditable,recoverable
HARDWARE maintained,protected from damage, secure from human tampering
SOFTWARE maintained & protected from security threats + vulnerabilities
What are some common database security threats?
privilege abuse
input injection
malware
storage media exposure
misconfigured databases
unmanaged sensitive data
denial of service
What is privilege abuse?
excissive privilege
e.g. employee only need read records but given write permissions
downloading data onto (less secure) local machines
How can we minimise the risk of privilege abuse?
grant minimal privelege to users
How are access controls managed in PostgreSQL?
assign users roles (roles = diff. attributes that fine its privileges)
e.g. roles required ro be assigned to perform taks like database creation
CREATE ROLE joe LOGIN;
superusers bypass all permission checks
access to database pbjects via commands that grant permissions
GRANT UPDATE ON Account to joe;
What is input injection?
flaws introduced when developers create dynamic database queries that include user supplied input
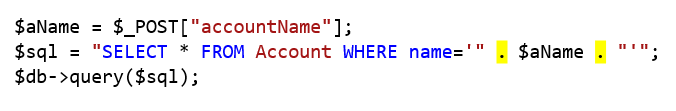
Why should you never use this style of code to query a database?
(using string concatenation (.) to build SWL statements in dynamic application code)
text that is valid SQL can be passed via thge inpit value
What are ways to prevent input injection?
parameterise queries
use stored procedures - parameterises your code for you
input validation
escape all input

How can malware be a risk to database security?
may be present on a remote device accessing DB
How can the malware risk be mitigated?
install anti malwate tools + keep them updated
keep application software updated
staff education
What is storage media exposure as a database security risk?
when backup media is completely unprotected from unauthorised access
How can the storage media exposure risk be prevented?
prevent unauthorised physical access to server (restrict acces to server room)
How can the misconfigured databases risk be prevented?
make sure default accounts are secure (e.g. for some versions of MySQL there is no root password on installation, so create one)
How can you prevent the risk of unmanaged sensitive data?
prevent external & internal access to the most sensitive data by encryption
What are the 2 main types of database encryption?
data at rest
encrypt data stored on a physical device
diff, options (e.g. full disk encryption, DB encryption)
data in transit
encrypting data being transmitted over a network
What is client level encryption?
encrypting data at client side (e.g. application before it is transmitted to DB server for storage)
server never sees unencypted data/access key
only intended recipient can decrypt data using access key
necessary for storing sensitive data in the cloud
What measures are put in place in order to prevent database security risks when storing passwords?
limit number of repeated qurrries
prevent brute force attacks
when wrong password entered
hash password columns
still susceptible to rainbow attack(precomputed reverse table applied to hash values)
vulnerable to dictionary attacks from lists of known passwords
use a salt
long unique random string appended to each stored password
use soemthing stronger than MD5
What is salting passwords?
for each stored password generate unique salt
combine salt wih password
hash combined salt + password
store salt & hashed salt & password combination
What is a denial of service (DoS) attack?
attempt to make server unavailable for legit users
lots of devices w/ spoofed IP addresses send excessive no. requests to server at same time
blocks/severly slows legit data requests
How are DoS attacks mitigated?
well configured firewall
excess bandwidth,CPU & memory capacity
distributed provision
What is included in effect database administration?
schedule software updates regularly
implement audit trails
track user activity (particuarly those w/ highest privilege)
physicallt secure server & backup media
configure DBMS & DBs properly
DBA should go on regular training courses to keep up to date w/ latest security issues