PT+ 5 · Test Logic, Web & AD Attacks
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/28

There's no tags or description
Looks like no tags are added yet.
29 Terms

Incident response order
Contain, Eradicate, Recover; immediate action = isolate or shut down first

Root-cause question strategy
Fix the actual flaw (e.g. quote the service path), not a compensating control
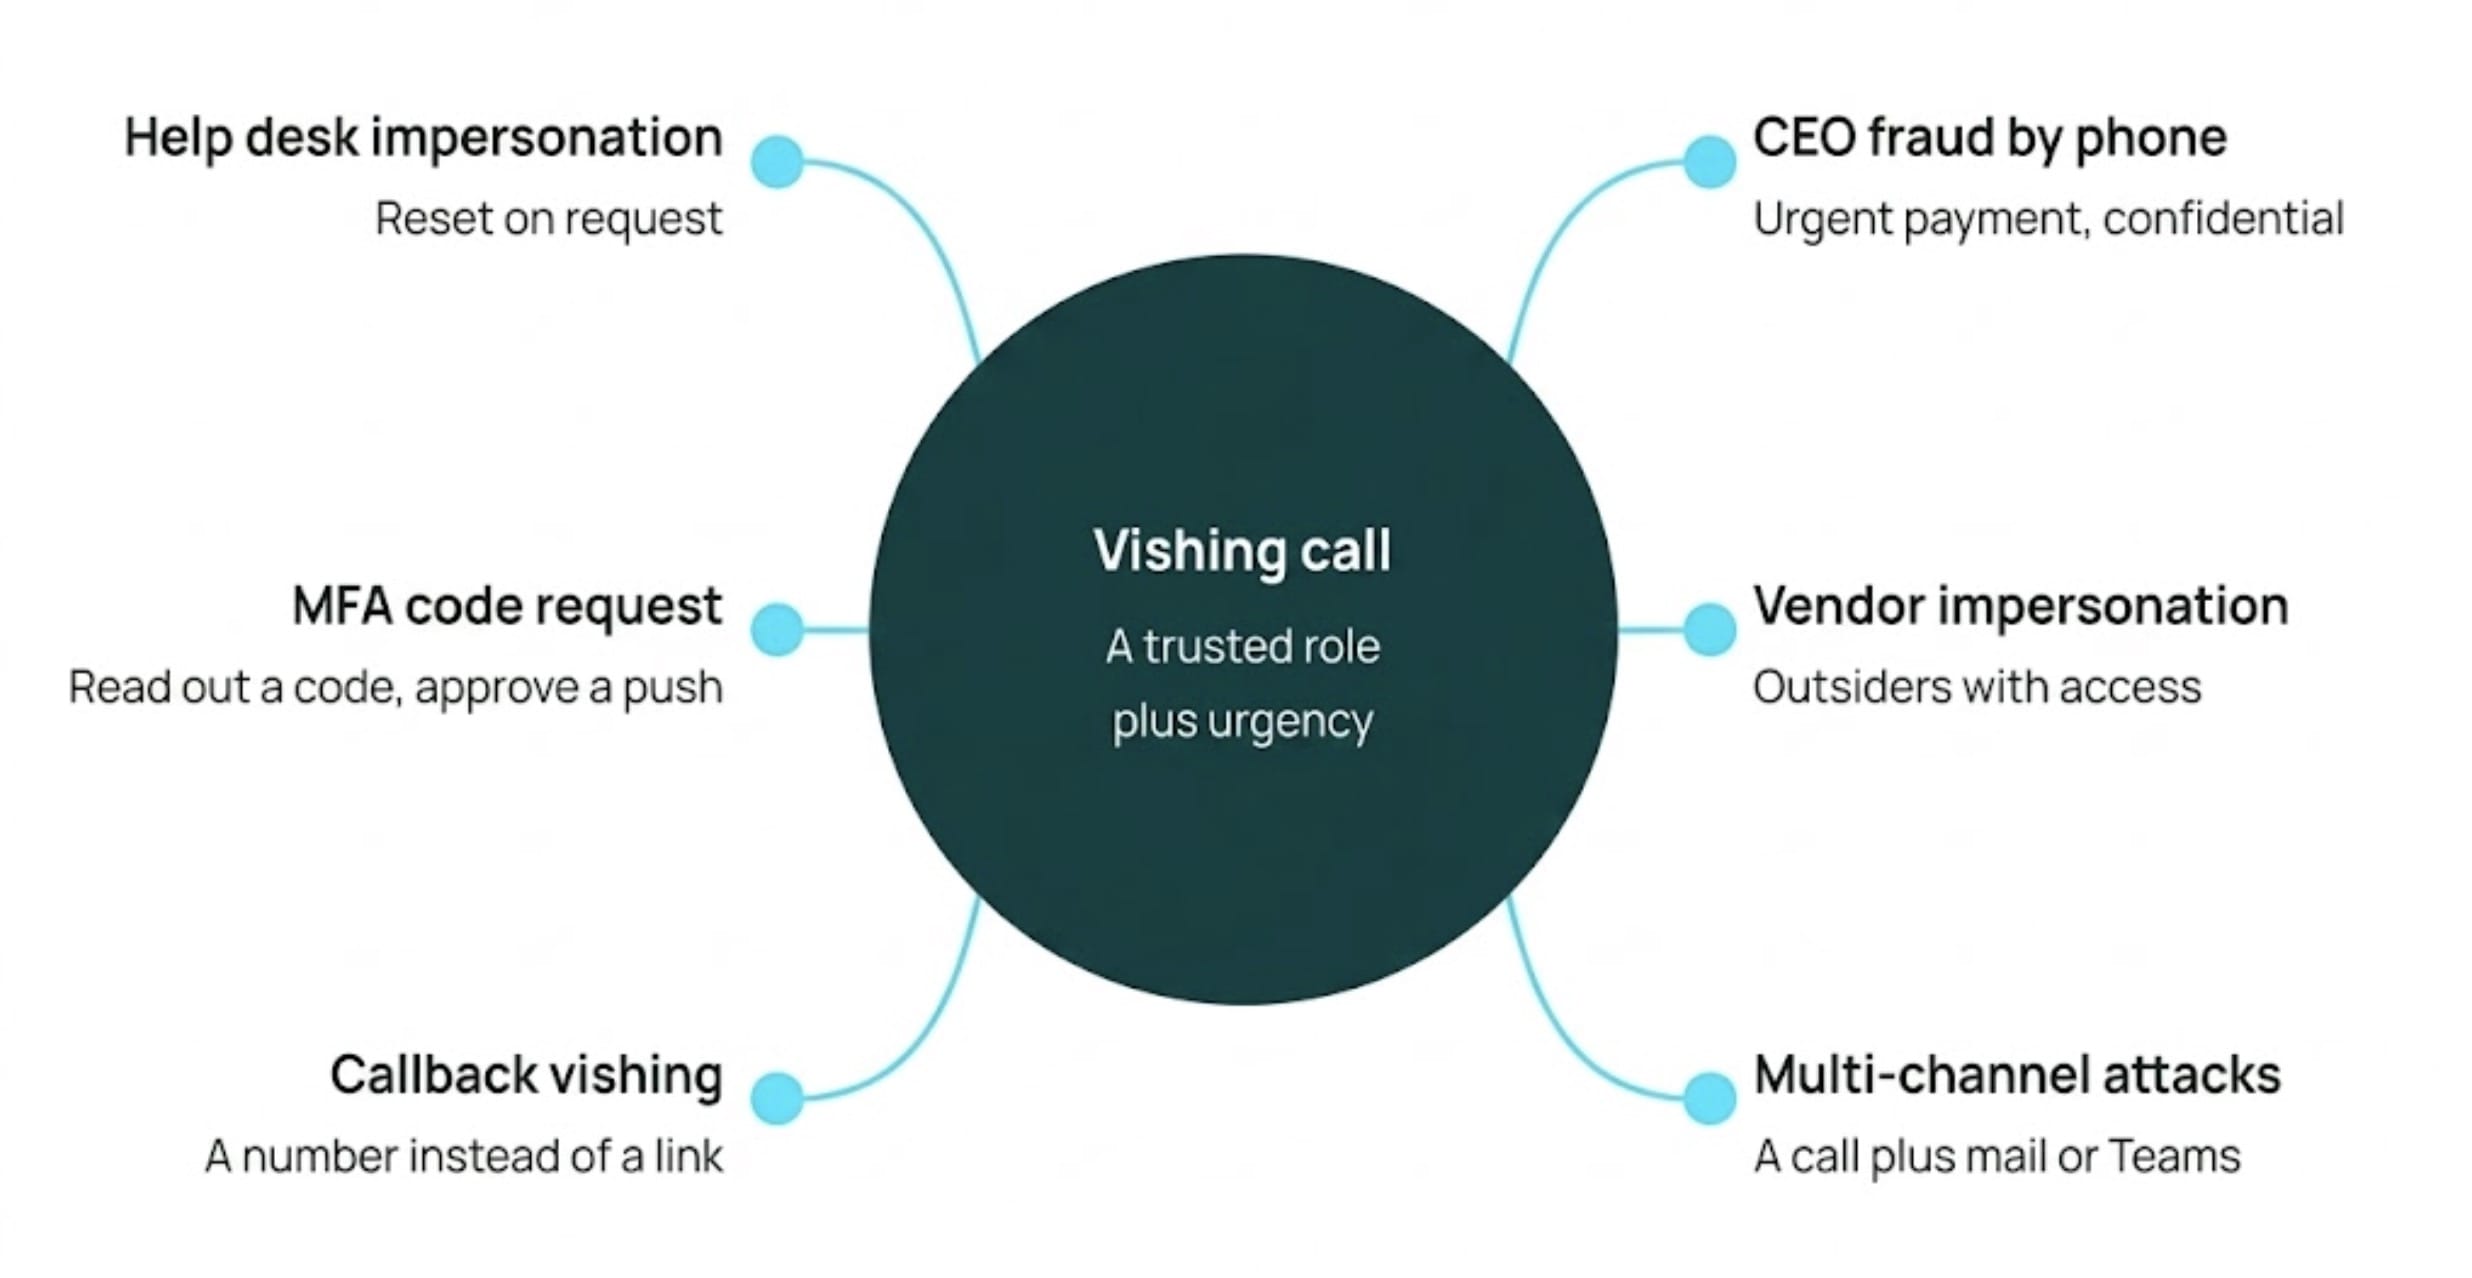
Impersonation vs vishing
Assuming a specific identity = impersonation, even over the phone; vishing = the channel

CSRF mitigation
Anti-CSRF token (not WAF or output encoding)

XSS mitigation
Output encoding / sanitize input
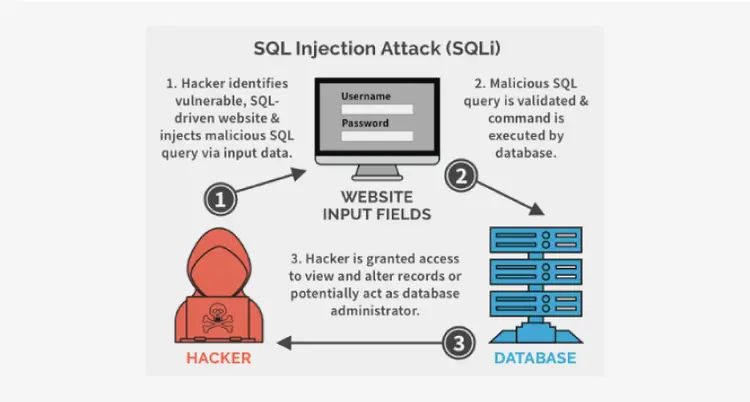
SQL injection mitigation
Parameterized (prepared) queries

Kiosk escape cleanup
Restore from a known-clean image

Load balancer misdirecting probes
Target individual server IPs directly

Testing firewall rules
Send crafted packets with hidden payloads on allowed ports
Scan clean but manual finds vulns
Scan misconfiguration

IDOR
Manipulate a URL or parameter value to access resources you don't own

CSRF
Trick an authenticated browser into an unwanted request

Stored vs reflected injection
Stored persists (saved comment); reflected only in the current session
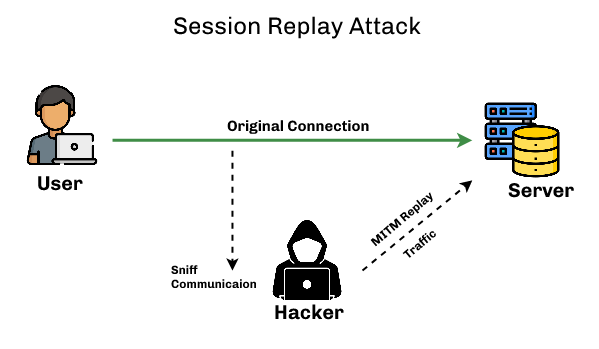
Session replay vs fixation
Replay = capture and reuse a valid session ID; fixation = force a known session ID

Issuing JWTs requires
Access to the private key that signs tokens

Kerberoasting steps
Get SPNs, extract service tickets, crack offline

AS-REP roasting targets
Accounts without Kerberos pre-authentication

Credential stuffing defense
Password manager (unique passwords per site)

Trust relationship abuse
Exploit trust between cloud services/roles to escalate privileges

Metadata service attack
Abuse the instance metadata endpoint (often via SSRF) to steal IAM creds

Kernel-level rootkit
Hides in device drivers; intercepts system calls
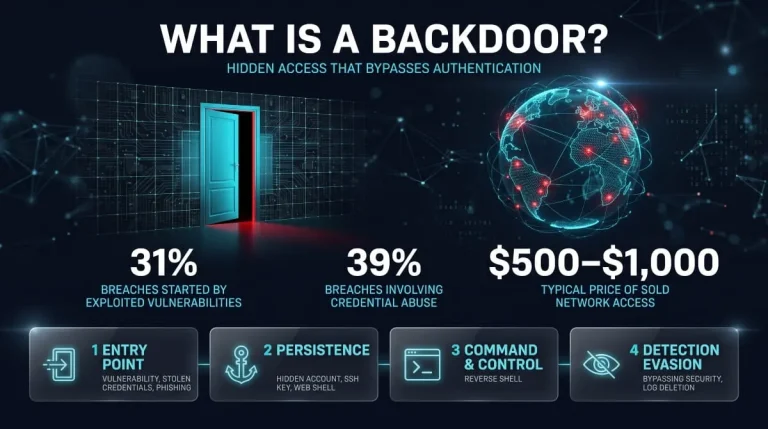
Persistence surviving reboot and always on
Custom Windows service set to auto-start

Lateral movement timing
Considered once at least one system is compromised

WMI
Enumerate system info and remote exec

WinRM
Remote PowerShell (ports 5985/5986)

PsExec
Run a remote command over SMB with admin creds

LOLBins
Signed built-in OS tools abused by attackers
Linux daemon
Equivalent of a Windows background service
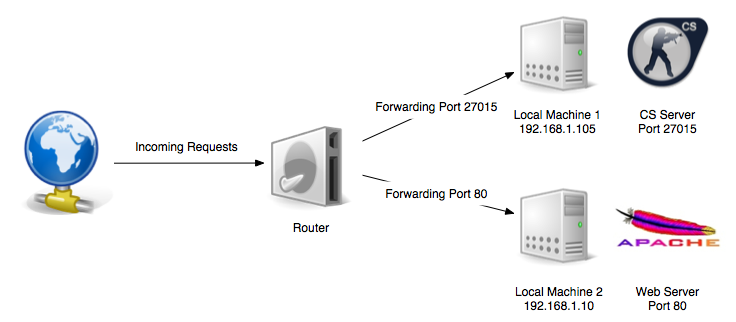
Port forwarding
Pivot traffic from a foothold to another subnet