Chapter 1: Today's Security Professional
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/79

There's no tags or description
Looks like no tags are added yet.
80 Terms
Matt is updating the organization's threat assessment process. What category of control is Matt implementing?
Managerial
Jade's organization recently suffered a security breach that affected stored credit card data. Jade's primary concern is the fact that the organization is subject to sanctions for violating the provisions of the Payment Card Industry Data Security Standard. What category of risk is concerning Jade?
Compliance
Chris is responding to a security incident that compromised one of his organization's web servers. He believes that the attackers defaced one or more pages on the website. What cybersecurity objective did this attack violate?
Integrity
Gwen is exploring a customer transaction reporting system and discovers the table shown here. What type of data minimization has most likely been used on this table?
Masking

Tonya is concerned about the risk that an attacker will attempt to gain access to her organization's database server. She is searching for a control that would discourage the attacker from attempting to gain access. What type of security control is she seeking to implement?
Deterrent
Greg is implementing a data loss prevention system. He would like to ensure that it protects against transmissions of sensitive information by guests on his wireless network. What DLP technology would best meet this goal?
Network-based
What term best describes data that is being sent between two systems over a network connection?
Data in transit
Tina is tuning her organization's intrusion prevention system to prevent false positive alerts. What type of control is Tina implementing?
Technical control
Which one of the following is not a common goal of a cybersecurity attacker?
Allocation
Tony is reviewing the status of his organization's defenses against a breach of their file server. He believes that a compromise of the file server could reveal information that would prevent the company from continuing to do business. What term best describes the risk that Tony is considering?
Strategic
Which one of the following data elements is not commonly associated with identity theft?
Frequent flyer number
What term best describes an organization's desired security state?
Control objectives
Lou mounted the sign below on the fence surrounding his organization's datacenter. What control type best describes this control?
Deterrent

What technology uses mathematical algorithms to render information unreadable to those lacking the required key?
Data encryption
Greg recently conducted an assessment of his organization's security controls and discovered a potential gap: the organization does not use full-disk encryption on laptops. What type of control gap exists in this case?
Preventive
What compliance regulation most directly affects the operations of a health-care provider?
HIPAA
Nolan is writing an after action report on a security breach that took place in his organization. The attackers stole thousands of customer records from the organization's database. What cybersecurity principle was most impacted in this breach?
Confidentiality
Which one of the following objectives is not one of the three main objectives that information security professionals must achieve to protect their organizations against cybersecurity threats?
Nonrepudiation
Which one of the following data protection techniques is reversible when conducted properly?
Tokenization
Which one of the following statements is not true about compensating controls under PCI DSS?
Controls used to fulfill one PCI DSS requirement may be used to compensate for the absence of a control needed to meet another requirement.
What are the three complementary objectives of a cybersecurity program, collectively known as the CIA triad?
Confidentiality, Integrity, and Availability.
In the CIA triad, what is the principle of Confidentiality?
It ensures that unauthorized individuals are not able to gain access to sensitive information.
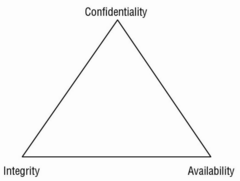
Firewalls, access control lists, and encryption are security controls primarily used to enforce which principle of the CIA triad?
Confidentiality.
What is the goal of Integrity in the CIA triad?
To ensure that there are no unauthorized modifications to information or systems, either intentionally or unintentionally.
Hashing and integrity monitoring solutions are examples of controls that seek to enforce which part of the CIA triad?
Integrity.
What does the Availability principle of the CIA triad ensure?
It ensures that information and systems are ready to meet the needs of legitimate users at the time they request them.
Fault tolerance, clustering, and backups are controls designed to ensure which objective of the CIA triad?
Availability.
What important cybersecurity goal, while not part of the CIA triad, ensures that someone cannot deny having taken an action?
Non-repudiation.
What common technology is used to provide non-repudiation, allowing confirmation that a message truly originated from its purported sender?
Digital signatures.
What are the three key threats to cybersecurity efforts, collectively known as the DAD triad?
Disclosure, Alteration, and Denial.
The threat of Disclosure, the exposure of sensitive information to unauthorized individuals, is a direct violation of which CIA triad principle?
Confidentiality.
What term describes the act of attackers gaining access to sensitive information and removing it from an organization?
Data exfiltration.
The threat of Alteration, the unauthorized modification of information, is a violation of which principle of the CIA triad?
Integrity.
The threat of Denial, which disrupts an authorized user's legitimate access to information, violates which principle of the CIA triad?
Availability.
What type of risk involves monetary damage to an organization, either directly from recovery costs or indirectly from lost revenue?
Financial Risk.
What type of risk occurs when negative publicity surrounding a security breach causes a loss of goodwill among customers and stakeholders?
Reputational Risk.
What type of risk threatens an organization's ability to become less effective in meeting its major goals and objectives as a result of a breach?
Strategic Risk.
What category of risk pertains to an organization's ability to carry out its day-to-day functions, possibly causing inefficiency and delays?
Operational Risk.
A security breach that causes an organization to violate legal or regulatory requirements, such as HIPAA, falls into what risk category?
Compliance Risk.
What term describes statements of a desired security state that an organization wishes to achieve?
Control objectives.
What are the specific measures that fulfill the security objectives of an organization called?
Security controls.
A _____ is a process where a cybersecurity professional reviews control objectives and examines the controls designed to achieve them to find any deficiencies.,gap analysis?
What category of security control enforces confidentiality, integrity, and availability in the digital space, such as firewall rules and encryption?
Technical controls.
What category of security control includes processes put in place to manage technology securely, such as user access reviews and log monitoring?
Operational controls.
What category of security control consists of procedural mechanisms focused on the risk management process, like periodic risk assessments and security planning?
Managerial controls.
Security controls that impact the physical world, such as fences, locks, and fire suppression systems, belong to which category?
Physical controls.
What type of security control intends to stop a security issue before it occurs, with firewalls and encryption being common examples?
Preventive control.
What type of security control seeks to prevent an attacker from attempting to violate security policies, such as a 'Beware of Dog' sign or barbed wire?
Deterrent control.
What type of security control is designed to identify security events that have already occurred, such as an intrusion detection system?
Detective control.
What type of security control remediates security issues that have already happened, like restoring backups after a ransomware attack?
Corrective control.
What type of security control is designed to mitigate risk associated with exceptions made to a security policy?
Compensating control.
Policies and procedures that inform employees what they should do to achieve security objectives are examples of what type of control?
Directive control.
According to PCI DSS, a compensating control must meet the _____ and rigor of the original requirement.
intent
What term describes stored data that resides on hard drives, tapes, or other storage media?
Data at rest.
What term describes data that is in motion over a network and is vulnerable to eavesdropping?
Data in transit.
What term describes data that is actively being processed by a computer system, such as data stored in memory?
Data in use.
What technology uses mathematical algorithms to protect information from unauthorized access, both in transit and at rest?
Encryption.
What type of system helps organizations enforce information handling policies to prevent data loss and theft by monitoring systems and networks
Data loss prevention (DLP) system.
An _____ DLP system uses software agents installed on endpoints to search for sensitive information and monitor user actions.,agent-based
An agentless, or _____, DLP system is a dedicated device that monitors outbound network traffic for sensitive data.
network-based
DLP systems that watch for telltale signs of sensitive information, like numbers formatted as credit cards, are using what mechanism of action?
Pattern matching.
What DLP mechanism involves applying electronic tags to sensitive documents and then monitoring for unencrypted content containing those tags
Watermarking.
What is the cybersecurity technique of reducing risk by reducing the amount of sensitive information that is maintained
Data minimization.
The process of removing the ability to link data back to an individual, thereby reducing its sensitivity, is known as _____.
deidentification
What is the general term for transforming data into a format where the original sensitive information cannot be retrieved
Data obfuscation.
Which data obfuscation technique uses a function to transform a value into a corresponding hash value, making it irreversible?
Hashing.
An attacker computes the hashes of many possible values and checks if they exist in a data file. What is this attack called
Rainbow table attack.
Which data obfuscation technique replaces sensitive values with a unique identifier using a secure lookup table
Tokenization.
Which data obfuscation technique is reversible if the lookup table is maintained securely
Tokenization.
Which data obfuscation technique partially redacts sensitive information by replacing some or all sensitive fields with blank characters (e.g., 'XXX-XX-1234')?
Masking.
What type of access restriction limits access to resources based on the physical location of the user or system
Geographic restrictions.
What type of access restriction limits access to resources based on a user's role or level of authorization
Permission restrictions.
What network security strategy involves placing sensitive systems on separate networks with strict communication rules between them
Segmentation.
What network security strategy completely cuts a system off from access to or from outside networks
Isolation.
An employee leaving an unencrypted laptop containing sensitive data in a taxi is an example of what type of security incident threat
Disclosure.
A distributed denial-of-service (DDoS) attack against a website is an intentional violation of which principle of the CIA triad
Availability.
What is the most common impact on individuals when an organization suffers a data breach involving personally identifiable information (PII)
Identity theft.
The Health Insurance Portability and Accountability Act (HIPAA) is a compliance regulation that primarily protects what type of information
Protected health information (PHI).
Updating an organization's threat assessment process is an example of what category of control
Managerial control.
Tuning an intrusion prevention system to prevent false positive alerts is an example of what category of control
Technical control.