Chapter 12 Security+ SYS-701
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/48

There's no tags or description
Looks like no tags are added yet.
Name | Mastery | Learn | Test | Matching | Spaced | Call with Kai | Chat |
|---|
No analytics yet
Send a link to your students to track their progress
49 Terms
What do layers 1-3 of the OSI model do?
For media (physical, data link, network)
What do layers 4-7 of the OSI model do?
Transport through applications
What is a DMZ?
A network that is in between the internet and the LAN. Usually surrounded by 2 firewalls. Purpose is to protect lan from external traffic

What does fail-closed mean?
If a security device fails, then don’t allow traffic through
What is a network tap?
Devices used to monitor traffic
What does active & passive network tap mean?
Active —> powered
Passive —> no power
What is an inline network tap?
Has all traffic flowing through it
What are reputation services?
Services that monitor data to block malicious IP’s, domains, and hosts
What is SDN?
Software defined network
What is SD Wan?
Using multiple wan networks for reliability (like fiber + lte)
What is SASE?
Secure Access Service Edge - Cloud-based security + SD-WAN + VPN/Zero Trust concepts.
What is the Extranet
A private network that gives access to authorized access users to some resources
What does East/West traffic mean?
Traffic between systems inside a network
What does adaptive identity mean in the zero trust model?
Uses multiple data points like user/device/location to establish and identity
What is the different between agent and agentless network access control (NAC)?
Agent NAC requires software running on the device and does better job, agentless is more network based
What is bpdu guard
BPDU is message used in STP, and BPDU guard shuts down switch port if it receives that message to prevent network loops
What is a site-site VPN?
Network to Network VPN
What is full tunnel VPN?
When all network traffic is redirected through the vpn
What is a split-tunnel VPN?
Only organization traffic is done through VPN
What layer is IPSec?
Layer 3
Describe layout of a forward proxy?
Client —> proxy —> internet
Designed to proect data going out
Describe layout of a reverse proxy?
Client —> proxy —> webserver
Designed to protect traffic coming in, determines who can access recourses
What is a stateless firewall?
Examines individual packets and makes descions based on info in the packets (like source and destination IP, etc.)
What is a stateful firewall?
Tracks multiple packets and looks at the entire conversation before making a decision
What is a UTM device?
Unified threat management device - has firewall, ips/ids, url and email filtering, etc.
What is a honeynet?
A network of fake honeypots
What is a honeytoken?
A fake/trackable data, not to be confused with a honeyfile
What is DKIM?
digitally signs email.
What is SPF?
identifies authorized sending servers.
What is DMARC?
uses SPF + DKIM to decide what to do with unauthenticated email.
What are ephemeral keys?
temporary encryption keys created for a single session or short period.
What is an SNMP trap?
Like a monitoring alert
What is FIM?
File integrity monitoring
Secure ports
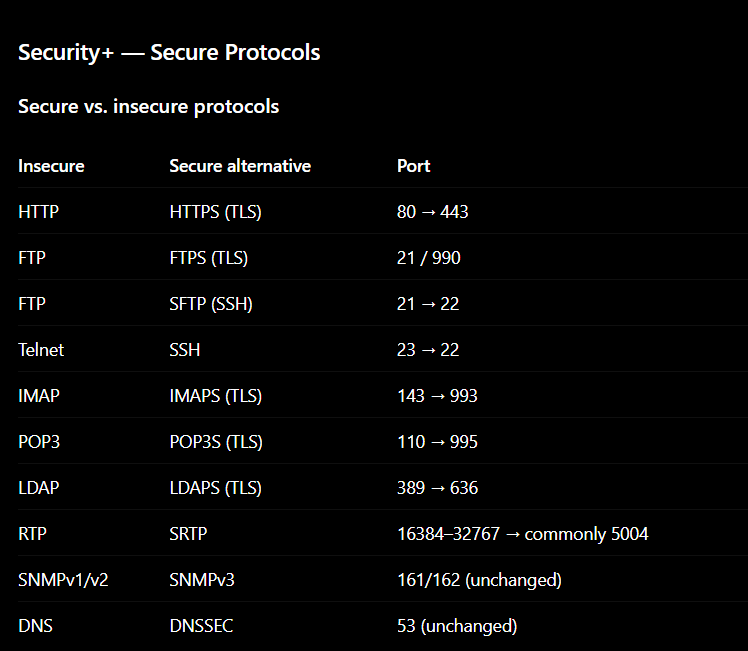
What is DNSSEC used for?
Digitally signs DNS records to verify authenticity and integrity. Does not encrypt DNS traffic.
What is required to make SNMPv3 secure?
authPriv
What is ESP?
Encapsulating Security Payload
What is transport mode in IPSec?
Protects the packet payload
What is tunnel mode in ip sec?
Protects the entire original IP packet by encapsulating it; commonly used for site-to-site VPNs.
How is NTP authentication secured?
Using NTS
What is SSL stripping?
Downgrades HTTPS connections to HTTP to expose traffic.
How can SSL stripping be combated?
By using HSPSTS - forces browsers to use HTTPS.
What is a SYN flood?
Sends TCP SYN requests without completing the handshake, exhausting resources.
What is amplification attack?
Small request generates a much larger response.
What is a reflection attack?
Spoofed victim IP causes third-party servers to send traffic to the victim.
What is a smurf attack?
Spoofed ICMP broadcast traffic overwhelms a victim.
What is xmas attack?
Uses unusual TCP flag combinations to probe or target systems.
What are on-path attacks?
take advantage of malicious browser plug-ins or proxies to modify traffic at the browser level.
What are PEP’s?
Policy enforcement points - Sits between user and resource rwards requests and enforces the access decision.