PT+ 6 · Specialty Attacks, Recon Facts & Ports
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/15

There's no tags or description
Looks like no tags are added yet.
16 Terms

Model evasion
Crafting inputs, such as subtly altered pixels, that make a trained classifier mislabel them.

CAN (Controller Area Network) bus message injection
Sending forged frames onto a vehicle's internal network to trigger actions like braking or unlocking.
Bluesnarfing
Stealing contacts, messages or files from a Bluetooth device without permission.

Bluejacking
Sending unsolicited messages to nearby Bluetooth devices; annoying, but it steals nothing.

DLL (Dynamic Link Library) injection first step
OpenProcess: getting a handle to the target before writing into its memory.
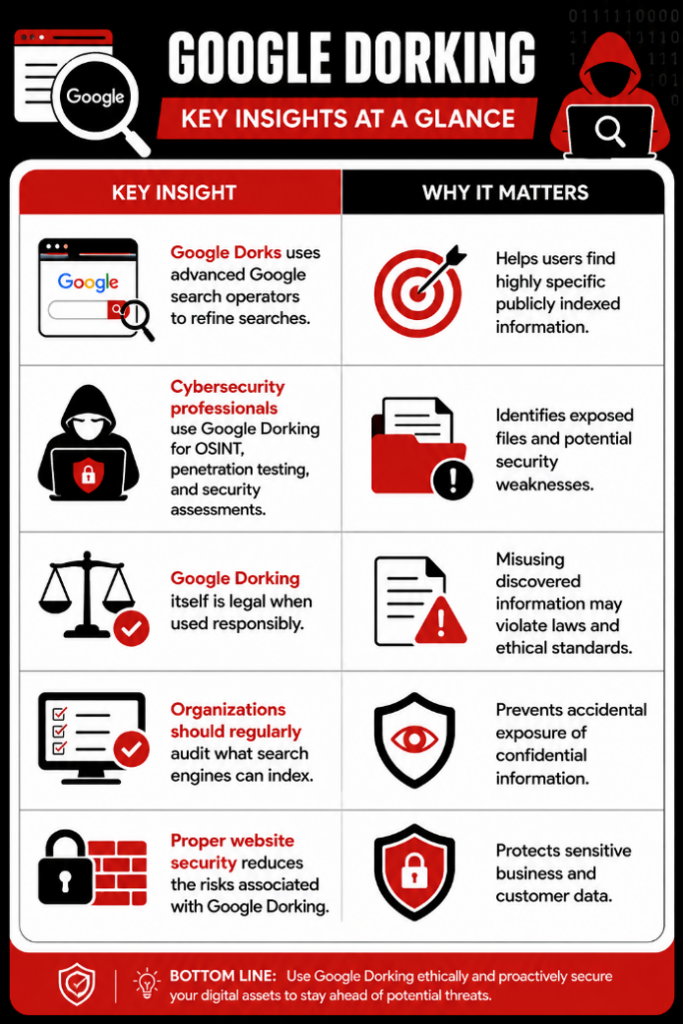
Google dork operators
Search modifiers like site:, filetype:, inurl: and intitle: that surface exposed files.
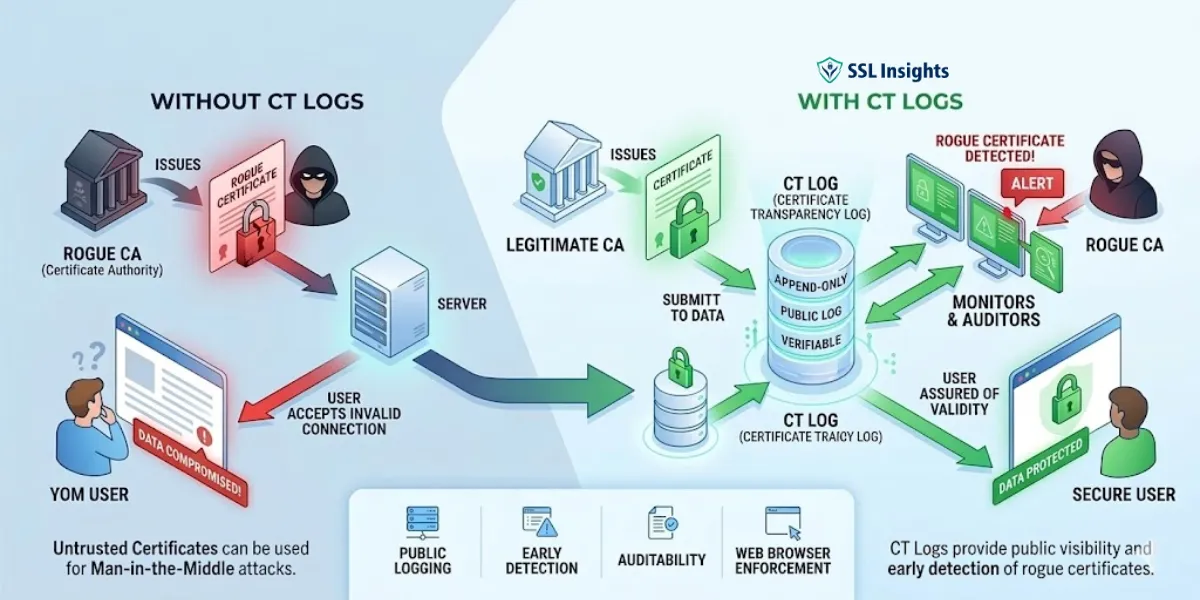
Certificate transparency logs
Public append-only records of issued TLS credentials, searched via crt.sh to uncover subdomains.
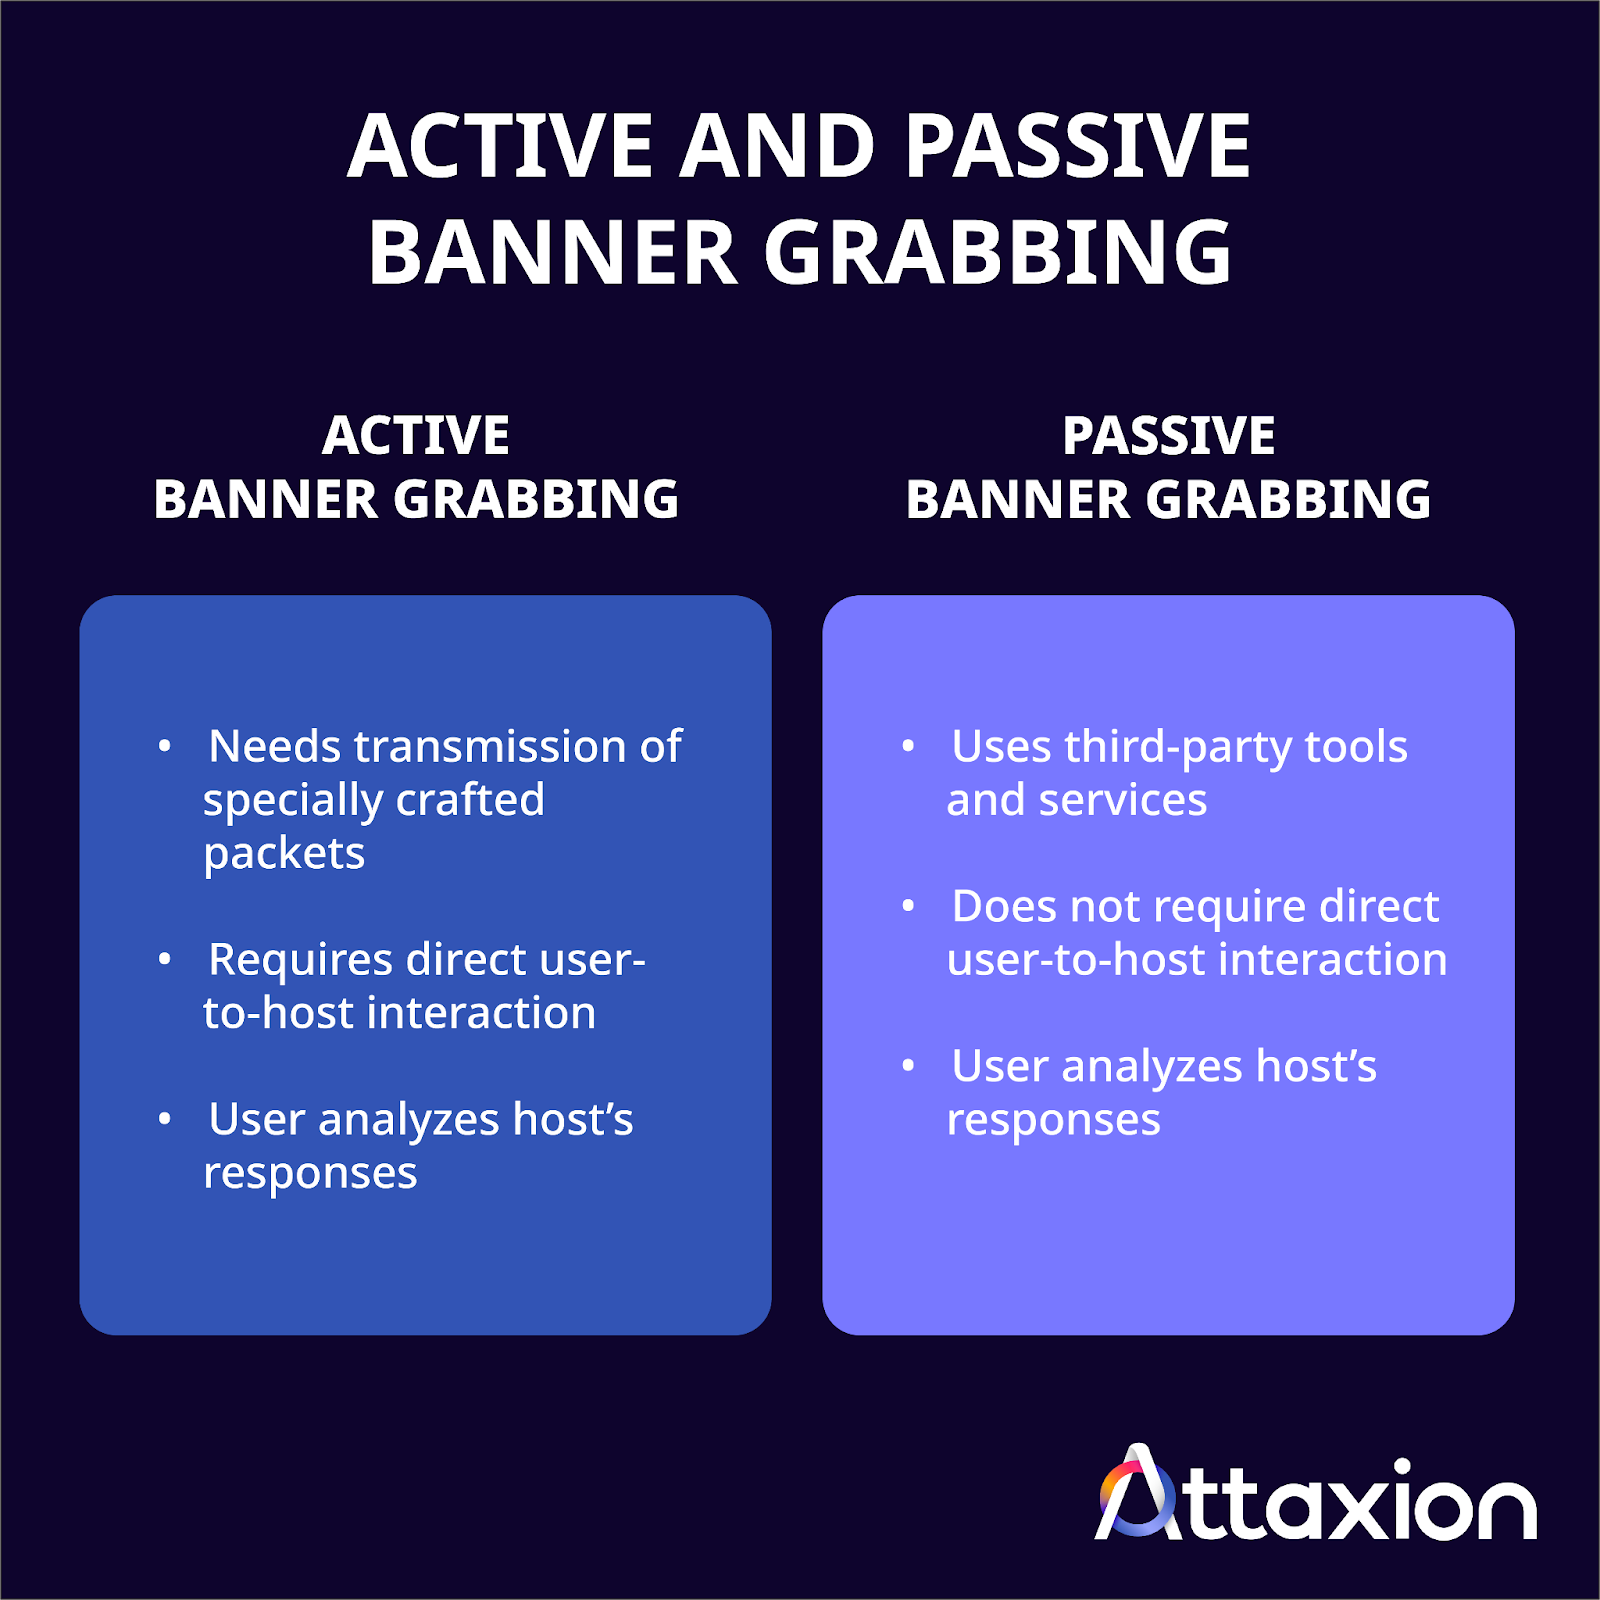
Banner grabbing tools
Connecting with Netcat or running nmap -sV to read a service's name and version string.

dig axfr
Command that asks a name server to hand over a full zone transfer.
Port 25
SMTP (Simple Mail Transfer Protocol) mail transfer between servers.

Port 445 / 139
SMB (Server Message Block) file sharing, with the lower port used by older NetBIOS sessions.
Port 3389
RDP (Remote Desktop Protocol) for graphical remote logins to Windows.

Port 389 / 636
LDAP (Lightweight Directory Access Protocol) directory queries, with the second port for the TLS-encrypted version.
Port 161
SNMP (Simple Network Management Protocol) device monitoring over UDP, often with default community strings.

Port 502
Modbus industrial control traffic over TCP, with no authentication.

WAF (Web Application Firewall) detection method
Checking responses for vendor-specific headers or cookies, like cf-ray from Cloudflare.