CPA ISC
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/341

There's no tags or description
Looks like no tags are added yet.
342 Terms
SOC 1 v SOC 2 reports
SOC 1 - Report on Controls at a Service Organization relevant to user entities’ ICFR.
SOC 2 - Report on Controls at a Service Organization relevant to Trust Service Criteria
SOC Type 1 v Type 2 Reports
Type 1 design + implementation of controls
Type 2 design + implementation of controls + operating effectiveness
Which SOC report provides the user with a basis for reducing the assessment of control risk below maximum?
Type 2
When can the user auditor refer to the service auditor’s report?
Unmodified opinion → no reference
Modified opinion → reference allowed to explain modification
Different Layers of IT infrastructure + examples
Hardware - servers
Software - financial reporting software
Network - internet, firewalls
Operating system - manages resources
Data storage - cloud
Data Storage Largest to Smallest
Largest: Data Lake - all structured + unstructured data
Smallest: Spreadsheets - tables
Example of Audit Data Analytics Tools
Data extracts + preparation
Data modeling
Data visualization
4 Types of ADA Techniques
Descriptive. What happened. Eg summary stats
Diagnostic. Why something happened. Relationships. Eg clustering
Predictive. What will happen in the future. Eg regression
Prescriptive. How to make something happen. Eg what if analysis
When a client’s IT system is extensively integrated, substantive evidence may not be available, so the auditor relies more heavily on ____
Test of controls
COSO Cube
3 objectives, 4 organizational structures, 5 internal control components
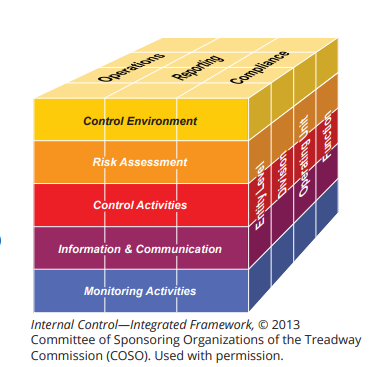
What are the components of the COSO framework? How many principles are there? What is the overarching component?
Control Environment. Ethics, BOD, organizational structure, competence, accountability
Risk Assessment. Specify objectives, identify risks, consider fraud, assess change
Information + Communication. Obtain info, internally + externally communicate
Monitoring Activities. Ongoing evaluations, communication of deficiencies
Existing Control Activities. Select + develop technology controls, deployment of policies + procedures
17 principles
Control Environment
Control Activities in a strong system of internal control?
PAID TIPS
Prenumbering of docs
Authorization of transactions
Independent checks
Documentation
Timely Reviews
Information Processing Controls
Physical Controls
Segregation of Duties
Segregation of Duties - 3 separate roles
Authorization
Record Keeping
Custody of Related Assets
Preventive v detective controls
Preventive - reasonable assurance that only valid transactions are processed. Before activity occurs. Eg segregation of duties, hiring competent individuals
Detective - errors discovered + corrected on a timely basis. After activity. Account reconciliations + monitoring
When to use manual v automated controls?
Manual - large, unusual transactions, judgement
Automated - high volume, recurring transactions
Limitations of IC
Management override
Human error
Collusion by 2+ people
External events beyond entity’s controls
What component of COSO do these principles relate to?
Ethics, BOD, organizational structure, competence, accountability
Control Environment
What component of COSO do these principles relate to?
Specify objectives, identify risks, consider fraud, assess change
Risk Assessment
What component of COSO do these principles relate to?
Obtain info, internally + externally communicate
Information + Communication
What component of COSO do these principles relate to?
Ongoing evaluations, communication of deficiencies
Monitoring Activities
What component of COSO do these principles relate to?
Select + develop technology controls, deployment of policies + procedures
Existing Control Activities
Creating policies and procedures is what category of COSO?
Existing control activities
Types of deficiencies
Control deficiency.
Design - control is missing or doesn’t achieve the desired objectives
Operation - does not operate at designed
Significant deficiency. Less severe than a material weakness yet important enough
Material weakness. Reasonable possibility that a material misstatement will not be prevented
Communication of deficiencies in internal control (Nonissuer)
ALL communication should be made within…
Control deficiency → management only, either orally or in writing
Sig deficiency + material weakness → management + those charged with governance in writing
ALL communication should be made within 60 days of report release date
Reperformance tests what about controls?
Operating effectiveness
What audit procedure needs to be combined with others to test operating effectiveness of controls?
Inquiry
What is audit risk? Formula
Risk the auditor may unknowingly fail to modify the opinion on FS that are materially misstated
AR = RMM x Detection Risk
RMM = inherent x control risk
Statements on Standards for Attestation Engagements (SSAE). Applies to?
AICPA. Attest. Examination, review, agreed upon procedures, report on a subject matter or assertion
How do attest standards differ from GAAS?
No reference made to historical FS
No reference made to GAAP
3 Types of Examinations + what they provide
Assertion-Based - positive opinion, high level of assurance
Direct examination - reasonable assurance by evaluating the subject matter against the criteria
Review - limited assurance.
Attest vs assurance what do you produce?
Attest → report
Assurance → opinion (reasonable)/ conclusion (limited)
Describe thse AICPA Code of Professional Conduct Rules:
Independence
Integrity + Objectivity
General Standards
Compliance with standards
Accounting principles rule
Confidential client info
Contingent fees
Acts discreditable
Advertising
Commissions
Forms of Org + Name
What are 3 of the most famous NIST frameworks?
Cybersecurity
Privacy
Security + Privacy controls
What is the CSF core?
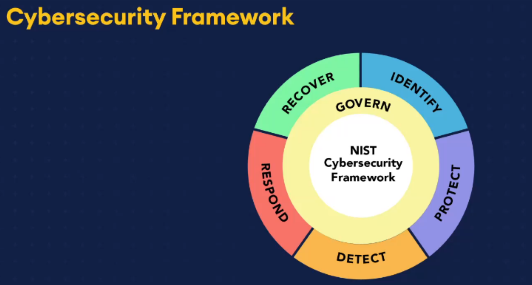
What are the 6 components of the core CSF?
Govern ID Protect Detect Respond Recover
Govern -
Identify - understand the risks
Protect - prevent a cybersecurity attack
Detect - timely discovery of attacks
Respond - how they manage the incident
Recover - returning to normal operations
What are the CSF tiers?
Subdivided into
Partial - reactive. Limtied awareness of risks
Risk-informed - cybersecurity processes isolated. Org aware but not consistent response
Repeatable - formal practices. Org wide approach
Adaptive - part of the culture. Actively adapts
Cybersecurity risk governance
Cybersecurity risk management
CSF Organizational Profiles
Current profile → currnet outcome
Taget profile → desired outcome
CSF Org Profiles 5 step approach
Some Guy Created AI
Scope the org profile
Gather the info needed
Create the org profile
Analyze the gaps between current + target
Implement the action plan + update
Overlap between Cybersecurity + Privacy framework

NIST Security Privacy 800-53 outlines 3 control implementation controls
Common Control → Implement controls at the org level
System-Specific Control → Info system level
Hybrid → Org level where appropriate + rest at info system level
What is the privacy law for the EU?
General Data Protection Regulation (GDRP)
What is a data breach? What are the 2 categories?
Data breach → exposure of confidential info to unauthorized persons
Unintentional → negiligence or error
Interntional → bad actors illegally gaining access
4 categories of expenditures for data breaches
Detection
Notifcation
Post-breach response - fix the breach
Loss of businesss + revenue
What is the Health Insurance Portability + Accountability Act (HIPAA)?
When can you disclose PHI, with no further authorization?
3 types of safeguards?
Governs the privacy of protected health info (PHI)
Individual
Treatment
With valid authorization
Admin safeguards - eg security training
Physical safeguards - eg facility access control
Technical safeguards - eg access control
HIPAA was amended by the Health Info Technology for Economic + Clinical Health (HITECH). What were the amendments?
Required that patients receive the option to obtain records in the electronic form
Added “business associates” as a covered entity
Notice of breach within 60 days after discovery
What data is subject to the Payment Card Industry Date Security Standard (PCI DSS)?
Cardholder data → account number, name, expiration data
Sensitive authetnication data → PIN + verification codes
PCI DSS Transaction Process

What does the security rule require covered entities to ensure for electronic protected health info (PHI)?
Confidentiality, integrity + availability
What type of additional processing is permitted under the GDPR purpose limitation principle?
Statistical analysis
What GDPR principle is clearly violates when a company collects extensive personal data from users that is not needed to complete a simple email newsletter signup?
Data minimization
How many CIS controls are there? They were designed with the following principles in mind:
18
Context - examples
Coexistence - aligning with industry standards
Consistency - minimal disruptions
What are the implementation groups?
Cybersecurity expertise
Data sensitivity
Can company sustain downtime/ biggest concern
IG1 → small or medium sized firms
Cybersecurity expertise limited
Data used is not sensitive
Company can’t sustain long periods of downtime
IG2 →
IT staff who support multiple departments
Data used is sensitive
Biggest concern → loss of trust
IG3 → large companies
Security experts in all domains
Data used is sensitive
Significant damage to company + public welfare
CIS Control 1 - Inventory + Control of Enterprise assets
Challenge
Control example
Helps org track + manage all IT assets
Challenge → portable decives that connect to a comp’s network then disappear
Establish + Maintain detailed asset inventory
CIS Control 2: Inventory + Control of Software Assets
Orgs can track + manage all software application + only authorized software installed
CIS Contol 3 Data Protection
Example control
Securely manage the entire life cycle of their data
Eg securely dispose of data
CIS Control 4 Secure Configuration of Enterprise Assets + Software
How can you protect?
Example
Helps org establish + maintain secure baseline configurations for their enterprise assets
Change default passwords
Implement and manage a firewall
CIS Control 5 Account Management
Example
Manage authorization for user accounts
Use unique passwords
CIS Control 6: Access Control Management
Example
Expands on Control 5
An org’s users should only have the necessary privileges required for their job role
Establish an access granting + revoking process
CIS Control 7: Continuous Vulnerability Management
What are unknown vulnerabilities?
Orgs must remain proactive in monitoring vulnerabilities
Unknown → occur when there is no known solution to a weak point
CIS Control 8: Audit Log Management
Types of logs?
Orgs can be alerted from attacks in real time
System logs → provide a list of events such as start and end time
Audit logs → tied to a specific user, eg when a person logs in and out
CIS Control 9: Email + Web Browser Protection
Example
How to detect + protect against cybercrime attempted through email
Ensure only fully supported browsers
Which CIS control best describes using processes + tools to create, assign + revoke access credentials for user + service accounts for enterprise assets + software?
Control 6: Access Control Management
CIS Control 10: Malware Defenses
What is living off the land?
Example
Helps companies prevent the installation of malware
Using an org’s existing tools against itself
Deploy Anti-Malware software
CIS Control 11: Data Recovery
Example
Data backups that allow orgs to recover company assets
Automated backups
CIS Control 12: Network Infrastructure Management
Example
Establishing procedures for securing a company’s network infrastructure
Ensure network infrastructure up to date
CIS Control 13 Network Monitoring and Defense
2 Common ways networks can be attacked
Example
Monitoring a network against internal + external security threats
Denial of Service → overwhelms a company’s network by flooding it with illegitimate requests so that it’s useless
Ransomware → attacker gains access to a company’s system, blcks employees from accessing, demand payment to regain access
Ransomware
Centralize security event alerting
CIS Control 14: Security Awareness + Skill Training
Example
Establishing a training awareness to reduce cybersecurity risk
Train workforce to recognize social engineering attacks
CIS Control 15: Service Provider Management
Example
Develop processes to evaluate third party service providers
Establish + maintain an inventory of service providers
CIS Control 16: Application Software Security
Example
Safeguards that manage the entire lifecycle of software
Establish + maintain a secure application development process
CIS Control 17: Incident Response Management
Example
Establish an incident response management program to detect, respond + prepare for cybersecurity attacks
Designate personnel to manage incident handling
CIS Control 18: Penetration Testing
Simulating actual attacks in an effort to find + exploit weaknesses
What is the Control Objectives for Info + Related Technologies
What version is it now? What was the version before?
What are the 2 unique disciplines?
Roadmap orgs can use to implement best practices for IT governance
COBIT 19… before COBIT 5
Governance → BOD
Management → CEO. Responsible for daily operations
Internal v external stakeholders
Internal → BOD + management
External → investors
How was COBIT 2019 developed?
COBIT 5
Six principles for a governance system
3 principles for a governance framework
Other standards + regulations
Community contribution
the COBIT core model is then customized through… __ ___ and ___ ___ to arrive at a…
Design factors + focus areas
Tailored enterprise governance system
What are the 6 principles for a governance system?
Value Holistic Dynamic Distinct Tailored End-to-end
Very Healthy Dieters Do Try Everything
Provide stakeholder value
Holitic approach
Dynamic governance system → relevant while adjusting to new challenges
Governance distrinct from management
Tailored to enterprise needs
End-to-end governance system
3 Principles for a Governance Framework
Based on a Conceptual model
Open + Flexible
Aligned to Major Standards
CFA
Governance objectives are grouped into how many domains?
1
Evaluate, Direct + Monitor (EDM)
Governance objectives are grouped into how many domains?
APO what is one of the most significant?
4
Align, Plan + Organize (APO) → managed data
Build, Acquire + Implement (BAI)
Deliver, Service + Support (DSS)
Monitor, Evaluate + Assess (MEA)
The COBIT model uses what 7 components to satisfy management + governance objectives:
CISO PPP
Culture, ethics + behavior
Info
Services, infrastructure + applications
Org Structure
Processes
Principles, policies + framework
People, skills + competencies
What are the COBIT 2019 publications?
Intro + Metholodology
Governance + Management Objectives
Design Guide
Implementation Guide
What is the AICPA’s trust services criteria?
CAPPS
Confidentiality
Availability
Privacy
Processing integrity
Security

What are EUDs?
End of User devices - computers that interact with employees or consumers
Examples of internal v external computer hardware
Internal → microprocessors
External →’mouse
What is network infrastructure?
Hardware, software, layout + topology of network resources that enable communication between devies on a computer network
What is a modem?
Modem connects a network to an internet service provider’s network, through a cable connection
What are routers?
Manage network traffic by connecting devices to form a network
Link between a modem and swtiches
Assign IP address
What are switches?
Divide devices within a computer network
Multiple devices can share one network connection
What is a gateway?
Computer or device that acts as an intermediary between different networks
Transfers data from 1 protocol into another so info can flow between networks
What are edge enabled devices?
Benefit?
Computing storage + networking functions to be closer to the devices where teh data request originates
Faster network response time
What are servers?
Physical or virtual machines that coordinate computers, programs + data
What are firewalls?
What is their purpose?
Protect a person’s network traffic by filtering it through security protocols
Prevent unauthorized access to the orgs
What are the types of firewalls?
Basic packet-filtering
Circuit-level
Application-level
Network address translation
Analyzes network traffic that is transmitted in packets
Verify the source of the packet
Inspect the packet iteself
Assign an internal network address to approxed external sources
What does topology mean? What is a bus topology?
Disadvantage?
Topology = physical layout
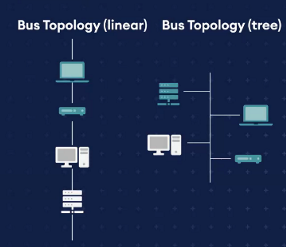
If central line is compromised, entire network goes offline
What is a mesh topology?
Disasdvantage
Numerous connections between nodes
Costly to implement + maintain

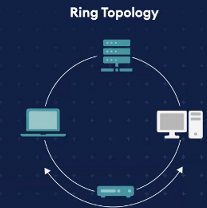
What is a ring topology?
Adv + dis
Nodes connected in a circular path
Adv: Data transmission collision is minimized
Dis: Slow network performance
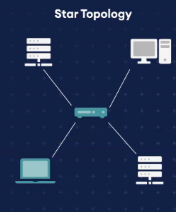
What is star topology?
Adv
data passes through a central hub that acts as a switch
Multiple hubs so if one fails, only nodes connected to hub will stop functioning. Makes it easy to identify damaged cables
What is the open systems interconnection model?
OSI explains how protocols work + how networking devices communicate with each other
What are the OSI model layers?
What is encapsulation
Moving down the layers → adding a header or footer to the data point received

What is the OSI application layer? Example
Interface between applications that a person uses + network protocol needed to trasmit a message
HTTP