A424 Exam 2
 Call Kai
 Learn
 Practice Test
 Spaced Repetition
 Match
 Flashcards
 Knowt Play
1/137

There's no tags or description
Looks like no tags are added yet.
138 Terms
Chapter 5
Part 1: Management assertions
Part 2: Evidence, Documentation, and Substantic Analytical Procedure
Relationship of audit evidence to audit report

Management assertions
Management is responsible for the fair presentation
of the financial statements in accordance with an accounting framework
Management assertions are expressed or implied representations by management regarding the recognition, measurement, presentation, and disclosure of information in the financial statements and related disclosures
Management assertions fall into 3 categories
assertions about classes of transactions and events for the period under audit & disclosures (income statement)
Assertions about account balances and disclosures at the period end (balance sheet)
PCAOB assertions
Management Assertions by Category

Assertions provide road map for the auditor
Assertions help the auditor determine what evidence to collect regarding various transactions, account balances, and required financial disclosures
Obtaining audit evidence to address all of the management assertions ensures “all bases are covered”
Management assertions constitute a powerful conceptual tool in the auditor’s toolbox
Possible misstatement = fictitious customer
Confirm accounts receivable - reach out to 3rd party
Testing existence
Possible misstatement = receivables have been sold or factored
inquire of management whether receivables have been sold
rights and obligations
Possible misstatement = customer accounts are not recorded
agree total of accounts receivable subsidiary ledger to accounts receivable control account
completeness
Possible misstatement = delinquent receivables carried at full amount
test the adequacy of the allowance for doubtful accounts (substantive testing)
Accuracy/valuation
Audit evidence
All the information, from whatever source, used by the auditor in arriving at the conclusions on which the audit opinion is based
collect evidence to test management’s assertions
3 concepts of audit evidence
nature of audit evidence
sufficiency and appropriateness of audit evidence
evaluation of audit evidence
Sufficiency of Audit Evidence - is there enough evidence to get reasonable assurance?
The measure of quantity of audit evidence
Greater risk of misstatement requires a higher quantity of audit evidence
Higher quality of audit evidence results in a lower quantity of audit evidence
Appropriateness of Audit evidence
measure of the quality of audit evidence
Relevance = the relationship to the assertion or to objective of the control being tested
reliability = whether a particular type of evidence can be relied upon to signal the true state of an assertion
What is reliability of audit evidence influenced by?
Reliability of audit evidence is influenced by its source and by its nature and is dependent on the circumstances under which it is obtained
Different circumstances under which audit evidence is obtained
Knowledgeable independent source of the evidence
External expert than client’s internal support
Effectiveness of internal control
Effective controls yield more reliable audit evidence
Auditor’s direct personal knowledge
Direct observation of evidence better than evidence obtained indirectly
Documentary evidence
Evidence that is tangible in document form better than oral presentation
Original documents
Original signed copies of agreements better than photocopies or pdf files
Three categories of audit procedures
Risk assessment procedures
Test of controls
Substantive procedures
Risk assessment procedures
Used to obtain an understanding of the entity and its environment, including its internal control, to assess the risk of material misstatement at the financial statement and relevant assertion levels
Test of Controls
Used to test the operating effectiveness of controls in preventing or detecting and correcting, material misstatements at the relevant assertion levels
Substantive procedures (the only way to find material misstatements)
Used to detect material misstatement at the relevant assertion level
Includes test of details and substantive analytical procedures
Types of audit evidence procedures
inspection of records or documents
inspection of tangible assets
observation
inquiry
confirmation
recalculation
reperformance
analytical procedures
scanning
Inspection of records and documents
Evidence obtained from external documents is more reliable than evidence obtained from internal documents
Vouching
Occurance/existence
Journal ledger → source documents
Tracing
Completeness
Source documents → Journal or Ledger
Inspection of tangible assets
Physical examination of a tangible asset
Observation
The process of watching a process or procedure being performed by others
Inquiry
In conducting inquiry, the auditor should
consider the knowledge, objectivity, experience, responsibility, and qualification of the individual to be questioned
ask clear, concise, relevant questions
use open or closed questions appropriately
listen actively and effectively
consider the reactions and response and ask follow-up questions
evaluate the response
Confirmation
The process of obtaining a representation of information or of an existing condition directly from a third party
The reliability of evidence obtained through confirmation is directly affected by factors such as…
the form of the confirmation
prior experience with the entity
the nature of the information being confirmed
the intended respondent
Information frequently confirmed by auditors and their sources of confirmation
cash balance → bank
AR → individual customers
Inventory on consignment → consignee
accounts payable → individual vendors
bonds payable → bondholders/trustee
common stock outstanding → registar/transfer agent
insurance coverage → insurance company
collateral for loans → creditors
Recalculation
Determining the mathematical accuracy of documents or records
Reperformance
The auditor’s independent execution of procedures or controls that were originally performed by company personnel
Analytical procedures
Evaluations of financial info made by a study of plausible relationships among both financial and nonfinancial dataS
Scanning
Review of accounting data to identify significant or unusual items
Guideline for reliability hierarchy of evidence
Lower reliability relationship generally observation and inquiry
Middle is inspection of records and documents, confirmation, analytical procedures, scanning
Higher reliability is inspection of tangible assets, reperformance, and recalculation
Flowchart
Filling the assurance bucket

Example of filling the assurance buckets for each assertion

Audit Documentation - Purpose
Provide support for the representation in the audit report (that the audit was conducted in accorance with GAAS)
Aid in the planning, performance, and supervision of the audit
Provide the basis for the review of the quality of the work (documents the evidence to support the auditor’s conclusions)
Purposes of Analytical Procedures
risk assessment procedures
substantive analytical procedures
final analytical procedures
Purpose of risk assessment procedures
Used to assist the auditor to better understand the business and to plan the nature, timing, and extent of audit procedures
Preliminary analytic - required for planning
Purpose of substantive analytical procedures
Used to obtain evidential matter about particular assertions related to business balances or classes of transactions
This is optional
Purpose of final analytical procedures
Used as an overall review of the financial information in the final review stage of the audit
Required for final review
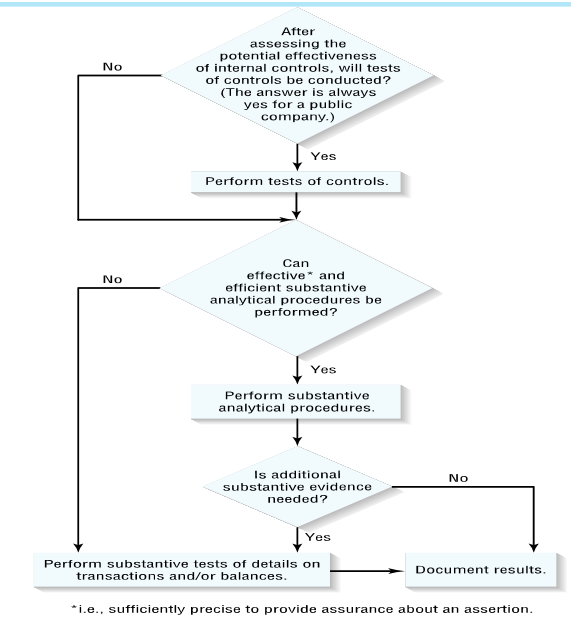
Substantive Analytical Procedures flowchart

Substantive Analytical Procedures - develop an expectation
Auditing standards require the auditor to have an expectation whenever analytical procedures are used. An expectation can be developed using a variety of information sources such as…
financial and operating data
budgets and forecasts
industry publications
competitor info
management’s analysis
analyst’s reports
Substantive Analytical Procedures - Define a tolerable difference
The size of the tolerable difference depends on
significance of the account
the desired degree of reliance on the substantive analytical procedures
the level of disaggregation in the amount being tested
the precision of the expectation
The amount is always less than overall materiality
Substantive Analytical Procedure - Compare and Investigate
Compare the expectation to the recorded amount and investigate any tolerable differences greater than the tolerable amount
Chapter 6
Internal controls in a Financial Statement Audit
Management is responsible for designing and maintaining a system of internal control that…
provides reasonable assurance that assets and records are properly safeguarded, and
the entity’s information system generates reliable information
Auditor is responsible for…
Obtaining an understanding of internal control
Assessing risk
(to design tests of control and substantive testing)
Internal control
A process designed and carried out by an entity’s board of directors, management, and other personnel to provide reasonable assurance about the achievement of the entity’s objectives in the following categories…
Reliability, timeliness, and transparency of internal and external, nonfinancial and financial reporting (auditor most concerned about the FR piece)
Effectiveness and efficiency of operations, including safeguarding assets
Compliance with applicable laws and regulations
ORC - Operations, Recording, Compliance
COSO Framework
Framework for creating and evaluating internal controls
5 Components (CRIME)
C - Control activities
R - Risk Assessment
I - Information
M - Montioring
E - Control Environment
Control Environment
Set of standards, processes, and structures that provide the basis for carrying out internal control across the organization. The board of directors and senior management establish the tone at the top regarding the importance of internal control and expected standards of conduct.
Control Environment Principle 1
The org demonstrates a commitment to integrity and ethical values
Ex: management should remove incentives and opportunities that might lead personnel to engage in dishonest, illegal, or unethical acts. Such as pressures to meet unrealistic performance targets
Control Environment Principle 2
Board of directors demonstrates independence from management and exercises oversight of the development and performance of internal control
Control Environment Principle 3
Management establishes, with board oversight, structures, reporting lines, and appropriate authorities and responsibilities in the pursuit of objectives
Specifically, management and the board should ensure that the entity’s reporting structure, reporting lines, and the division of authorities and responsibilities are such that the entity is able to provide timely, accurate, and reliable financial reporting
Control Environment Principle 4
The org demonstrates a commitment to attract, develop, and retain competent individuals in alignment with objectives
The entity should have sound personnel policies for hiring, orienting, training, evaluating, counseling, promoting, compensating, planning for succession, and taking remedial action. For example, an entity can demonstrate its commitment to hiring competent and trustworthy people by establishing standards that emphasize seeking the most qualified individuals, with emphasis on educational background, prior work experience, and evidence of integrity and ethical behavior.
Control Environment Principle 5
Org holds individuals accountable for their internal control responsibilities in the pursuit of objectives
Management and the board of directors also establish performance measures, incentives, and rewards appropriate for responsibilities at all levels of the entity, reflecting reasonable expectations for performance and standards of conduct in light of both short-term and longer-term objectives. It is also important that incentives and rewards be aligned with the fulfillment of internal control responsibilities. Finally, management and the board of directors should evaluate performance of internal control responsibilities, including adherence to standards of conduct and expected levels of competence, and provide rewards or exercise disciplinary action as appropriate.
Examples of control environment
“Tone at the top”
Elements include
corporate governance, the board of directors, and audit committee
organization-wide commitment to integrity and ethics
management operating style
organizational structure
commitment to financial reporting competencies
authority and responsibility
human resource policies
Risk assessment
Dynamic and iterative process for identifying and analyzing risks to achieving the entity’s objectives, thereby forming a basis for determining how risks should be managed.
Management considers possible changes in the external environment and within its own business model that may impede its ability to achieve its objectives.
Once risks have been identified, management should consider their significance, the likelihood of their occurrence, and how they should be mitigated through the implementation of controls.
Risk Assessment Principle 6
The org specifies objectives with sufficient clarity to enable the identification and assessment of risks relating to objectives
Objectives specific to external financial reporting include the preparation of financial statements for external purposes.
Risk Assessment Principle 7
The org identifies risks to the achievement of its objectives across the entity and analyzes risks as a basis for determining how the risks should be managed
Risk Assessment Principle 8
The organization considers the potential for fraud in assessing risks to the achievement of objectives
Fraud triangle
Risk Assessment Principle 9
The org identifies and assesses changes that could signficiantly impact the system of internal control
the entity considers the impact of changes to the regulatory, economic, and physical environment in which the entity operates, as well as new or dramatically altered business lines, rapid growth, changing reliance on foreign geographies, and new technologies. The organization also considers changes in management and resulting changes in attitudes and philosophies with respect to the system of internal control.
Risk assessment examples - the client’s business risks can arise or change due to the following circumstances…
changes in the operating environment
corporate restructuring
expanded international growth
new personnel
new technology
rapid growth
new accounting pronouncement
new info systems
new business models, products, or activities
Control Activities
Actions established by policies and procedures to help ensure that management directives to mitigate risks to the achievement of objectives are carried out. Control activities are performed at all levels of the entity and at various stages within business processes and over the technology environment
Basically these control activities support FR by addressing risks identified in the risk assessment process
Control activities Principle 10
Org selects and develops control activities that contribute to the mitigation of risks to the ahcievement of objectives to acceptable levels
performance reviews
independely check the performance of the individuals or processes in the system
physical controls
physical security of assets, authorization req to access computer programs, comparing cash and inventory counts w accounting records)
segregation of duties (Authorization, Recording, Custody)
Info processing controls
Segregation of duties example
Authorization: Approving a transaction → A manager approves a supplier’s invoice for payment.
Recording: Entering the transaction in accounting records → An accountant records the payment.
Custody: Handling or controlling assets → A treasury employee releases the payment from the bank account.
Purpose: Separate these duties so one person cannot both commit and conceal an error or fraud.
For example, if an employee receives cash payments on account from customers and has access to the accounts receivable subsidiary ledger, it is possible for that employee to misappropriate the cash and cover the shortage in the accounting records.
Control activities Principle 11
Org selects and develops general control activities over technology to support the achievement of objectives
Control activities Principle 12
Org deploys control activities through policies that establish what is expected and procedures that put policies into action
Control activies involve…
The design and operation of controls
Organizations use preventative and detective controls
Preventive controls: Stop errors or fraud before they occur.
Examples: Segregation of duties, required approvals, and password restrictions.Detective controls: Identify errors or fraud after they occur so they can be corrected.
Examples: Bank reconciliations, physical inventory counts compared with records, and reviews of unusual transactions.
Examples of control activities
segregation of duties
approval and co-signing agreements
documentation trails and pre-numbered sequence controls
restricted physical access
reconciliations
computerized controls for accounting info systems (data validation controls)
Information and communication
Info is necessary for the entity to carry out internal control responsibilites in support of achievement of its objectives
Communication occurs both internally and externally and provides the org w the information needed to carry out day-to-day internal control activities. Communication enables personnel to understand internal control responsibilites and their importance to the achievement of objectives
Info and communication principle 13
org obtains or generates and uses relevant, quality info to support the functioning of internal control
identify and record all valid transactions
classify transactions properly
measure the value of transactions properly
record transactions in the proper period
properly present transactions and disclosures
Info and communication principle 14
Org internally communicates info, including objectives and responsibilities for internal control, necessary to support the functioning of internal control
Info and communication principle 15
Org communicates w external parties regarding the matters affecting the functioning of internal control
Monitoring activities
Ongoing evaluations, seperate evaluations, or some combo of the two are used to ascertain whether each of the 5 components of internal control, including controls to effect the principles within each component are present and functioning. Findings are evaluated and deficiences are communicates in a timely manner, with serious matters reported to senior management and to the board
Could be by internal auditors and others
Montioring activities principle 16
Org selects, develops, and performs ongoing and/or separate evaluations to ascertain whether the components of internal control are present and functioning
For example, management might review whether bank reconciliations are being prepared on a timely basis and have the internal audit department review those reconciliations. To the extent that monitoring activities identify deficiencies in internal control, there must be processes in place to communicate those deficiencies in a timely manner to those parties responsible for taking corrective action, including senior management and the board of directors, as appropriate (Principle 17).
Montioring activities principle 17
Org evaluates and communicates internal control deficiencies in a timely manner to those parties responsible for taking corrective action, including senior management and the board of directors, as appropriate
Examples of monitoring
“controls over the controls”
employee hotlines to facilitate whistleblowing
an effective internal audit function
checks and reconciliations
Planning an audit strategy
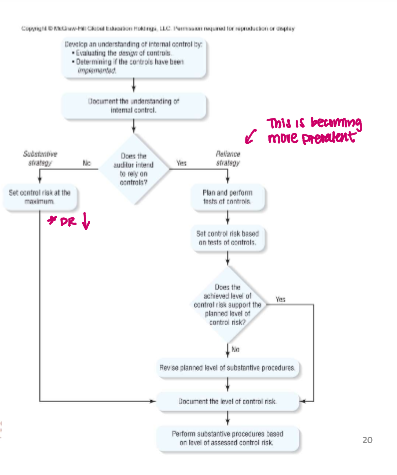
Steps to planning a audit strategy
Develop an understanding of internal control
Evaluate the design of controls
determine if controls have been implemented
document understanding
determine whether you intend to rely on the controls
No → substantive strategy
Set control risk at maximum, and only perform substantive testing
Yes -→ reliance strategy
Set control risk at moderate or low and perform tests of controls, and then perform substantive testing (less)
Perform substantive procedures based on the level of control risk
Consider a substantive strategy when one or all of the following exist:
controls do not pertain to an assertion
controls are assessed as ineffective (by design or operation)
testing of the effectiveness of controls is inefficient
Reliance strategy
means the auditor intends to rely on an entity’s controls
obtain an understanding of the internal control
plan and perform tests of controls
if test results indicate that achieved control risk is higher than planned → increase the planned substantive procedures and document the revised control risk assessment
if test results support the planned level of control risk, no revisions of the planned substantive procedures are required
Understanding of internal controls is used to…
identify types of potential misstatements
pinpoint the factors that affect the RMM
design tests of controls and substantive procedures
When obtaining an understanding, consider…
complexity and sophistication of operations and systems including IT systems
Use the following procedures to obtain an understanding of internal controls…
inquiries of management and entity personnel
inspection of eneity documents and reports
observation of entity activities and operations
Limitations of an entity’s internal control
management override of internal control
human errors or mistakes
collusion
cost prohibitive (esp for smaller entities)
When using a reliance strategy, set control risk at a lower level (mod or low), then…
identify specific controls that will be relied upon
perform tests of controls
test design and operaitng effectiveness
conclude on the achieved level of control risk
Example on the achieved level of control risk:

Chapter 7: Auditing Internal Control Over Financial Reporting
Background on audits of ICFR
Major accounting scandals occured in the late 1990s and early 2000s
Enron and Worldcom in late 2001 and early 2002 are the late straw for regulators
Demand for strong internal controls over the financial reporting to prevent fraud and errors
Demand for ) of internal controls over financial reporting
SOX 2002 & Internal controls related to publically traded companies
Management required to report on the effectiveness of its ICFR
Section 302 requires quarterly certifications
Section 404(a) requires annual report
External audit required on the effectiveness of ICFR (most issuers)
Section 404 (b) req an audit based on the PCAOB standards, Audit Standard No.5 (AS5)
AS5 guidance:
Integrated audits of ICFR and financial statements
Top-down, risk-based approach to evaluating ICFR
Dodd Frank Act of 2010 exempts smaller public companies, “non-acceleerated fillers” (common equity <75M)
Dodd-Frank Act of 2010
Exempts smaller public companies (common equity of <75M) from having to get ICFR audits, but many voluntarily get them to signal to investors that they are high quality.
Under Section 404, management is responsible for a management report that includes…
Their responsibiility for establishing and maintaining adequate ICFR
Their assertion on the effectiveness of ICFR as of the end of the fiscal year (“as of'“ assertion
If control deficiencies during the year are remediated prior to year-end, can still issue an unqualified “clean” report
Management must compy with the following requirements in order for the external auditor to complete an audit of ICFR
Accept responsibility for the effectiveness of the entity’s ICFR
Evaluate the effectiveness of the entity’s ICFR using suitable control criteria
Support the evaluation with sufficient evidence, including documentation
Present a written assessment regarding the effectiveness of ICFR at year-end
Auditor responsibilities under section 404
Audit management’s assertion about the effectiveness of ICFR
Objective of audit is “to express an opinion on the effectiveness of the company’s ICFR”
Plan and perform the audit to obtain reasonable assurance about whether the entity maintained, in all material aspects, effective internal control as of the date in management’s assertion
ICFR per AS5
A process designed by, or under the supervision of, the company’s principal executive and principal officers, or persons performing similiar functions, and effected by the company’s board of directors, management, and other personnel, to provide reasonable assurance regarding the reliability of financial reporting and the preparation of financial statements for external purposes in accordance with GAAP and includes those policies and procedures that…
ICFR per AS5…
Pertain to the maintenance of records that, in reasonable detail, accurately and fairly reflect the transactions and dispositions of the assets of the company
Provide reasonable assurnace that transactions are recorded as necessary to permit preparation of financial statements in accordance with GAAP and that reciepts and expenditures of the company are made only in accordance with authorizations of management and directors of the company
Provide reasonable assurance regarding prevention or timely detection of unauthroized acquisition, use, or disposition of the company’s assets that could have a material effect on the financial statements